.

Showing posts with label csrf vulnerability report.. Show all posts

Sunday, 14 December 2014

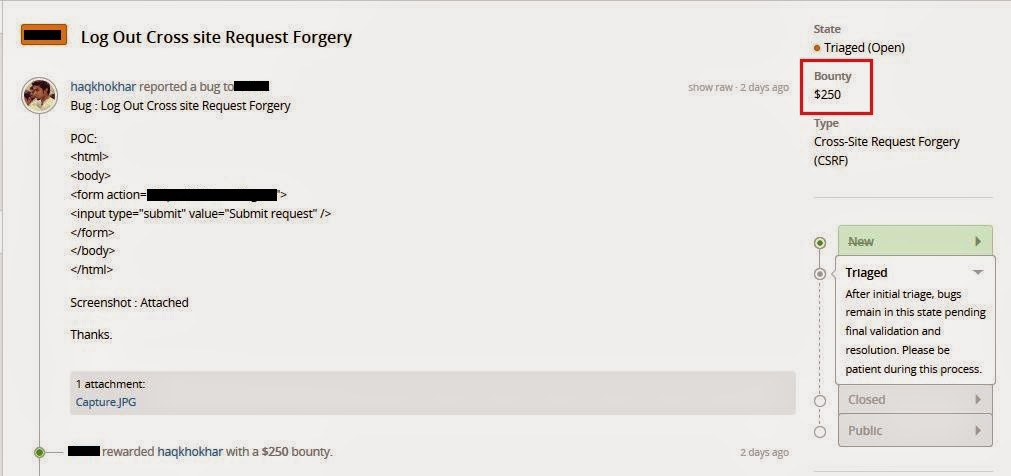
Logout Cross site Request Forgery CSRF Vulnerability [worth bug 250$ ]


CSRF LOGOUT IMPACT :


Logout should protect your logout mechanism against CSRF. At first it seems that all an attacker can do is logout the user, which would be annoying at worst. However, if you combine this with a phishing attack, the attacker may be able to entice the victim to re-login in using their own form and then capture the credentials. Very sketchy, but to protect against this sort of attack requires little cost.


LOGOUT CSRF POC :


Overview:

Hello , This is Abdul Haq Khokhar , I am Independent Security Researcher and I have recently found Vulnerability in website (Private Program) on hackerone.com and I don't want to disclose website because my report is still Triaged (12-12-2014) and security team is fixing now.

well vulnerability was really simple as i shown in below POC-Screenshot and i was just testing this vulnerability first time so i tried on this web and Got the Shocking response from the Website .


BUG : Logout CSRF Cross site Request Forgery CSRF


POC Code :
Already shown in POC Screenshot above .

Reporter : Abdul Haq Khokhar

After Reading the Response from Security team :

Reward :
250$


I hope you enjoyed this article and Hopefully you guys will try this bug on other websites too :-D


“Let him who would enjoy a good future waste none of his present.”
Roger Babson

For Contact :

Facebook  | Twitter  |  Bugcrowd  | Hackerone        


Read more ...

Friday, 21 November 2014

How to Takover the Account by Simple Trick[Bug,csrf Protection]


Vulnerability type 
 InSecure Direct Object Reference

How to Takeover the Account Via Simple Trick :

Someone researcher found the account takeover vulnerability in Private website and so you can consider someone is me.so let me start how to takeover the account in simple way .i was testing the website and then i got an account editing page so as always tried to find csrf vulnerability and after some hardwork i bypassed their mechanism of CSRF protection by deleting the authenticity_token= value from the editing request ! But wait what is it ?


 After lots of hard-work i see the edit page So by changing the value in the id=edit_account_<victim_id> I was able to change the details of victim and also able to delete the account from the website.


Vulnerability Fixed :Within 2 days the “secret” website fixed the bug !But maybe I should check it again!

OMG ! They plugged some internal protection but they didn’t change anything in the POST request’s functionality!


So let's try for second time :D !


May be I should try to changing the parameter’s value id=<edit_account_victim_id> to id=<victim_id>

Done so I bypassed the mechanism of website second time also :) !


They rewarded me some more bounty ! 


If you want any question so feel free to ask on comment .


Read more ...

About

Like Us